Skip to content Skip to footer

Client project for Hamdiservices

GitOps delivery for a Next.js platform

A GitLab-integrated CI/CD and GitOps pipeline for a Next.js blog platform on RKE2: build, test, scan and roll out with Argo CD, just like in production.

Project

Client project for Hamdiservices

Focus areas

CI/CD, GitOps, security

Technologies

GitLab CIArgo CDKustomizeTrivyOWASP ZAPDockerRKE2TraefikLonghornNext.jsMongoDB

Overview

The application is a Next.js blog with MongoDB and NextAuth.js. The goal was a production-like setup: build, test and scan containers in GitLab CI, then hand deployment over to Argo CD through a clean GitOps model.

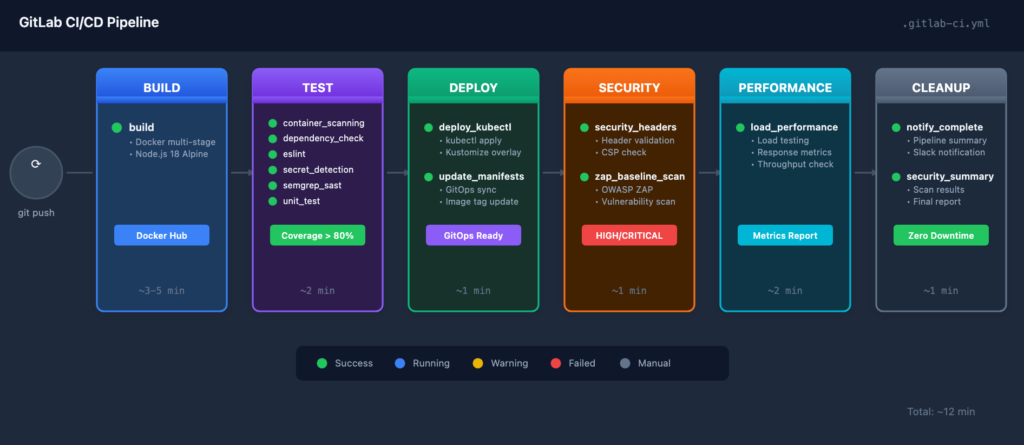
The pipeline runs 14 jobs in 6 stages, including Trivy container scanning, SAST, secret detection and OWASP ZAP baseline scans. Kustomize overlays separate dev and prod.

Implementation

  1. Push triggers the pipelineEvery push to the GitLab repository starts the pipeline: build, test, deploy, security scan, performance and cleanup.
  2. Build and push the imageMulti-stage build on Node.js 18 Alpine, pushed to Docker Hub (elmehdi74/blog-rke2) with latest and version tags. Final size about 156 MB.
  3. Update GitOps manifestsAfter the tests pass, the pipeline updates the Kustomize manifests in the GitOps repository.
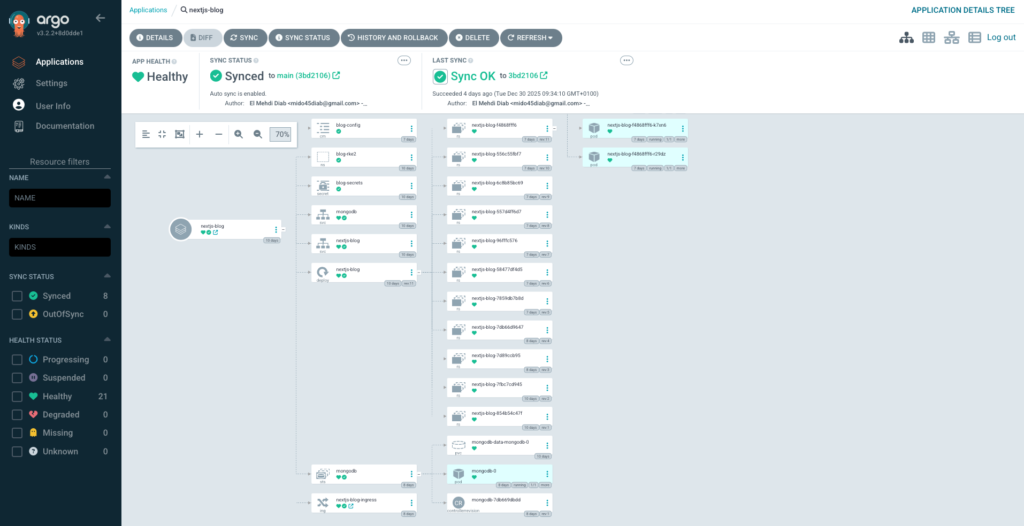
  4. Argo CD syncsArgo CD v3.2.2 picks up the change and reconciles the cluster automatically, with auto-sync, self-healing and one-click rollback.
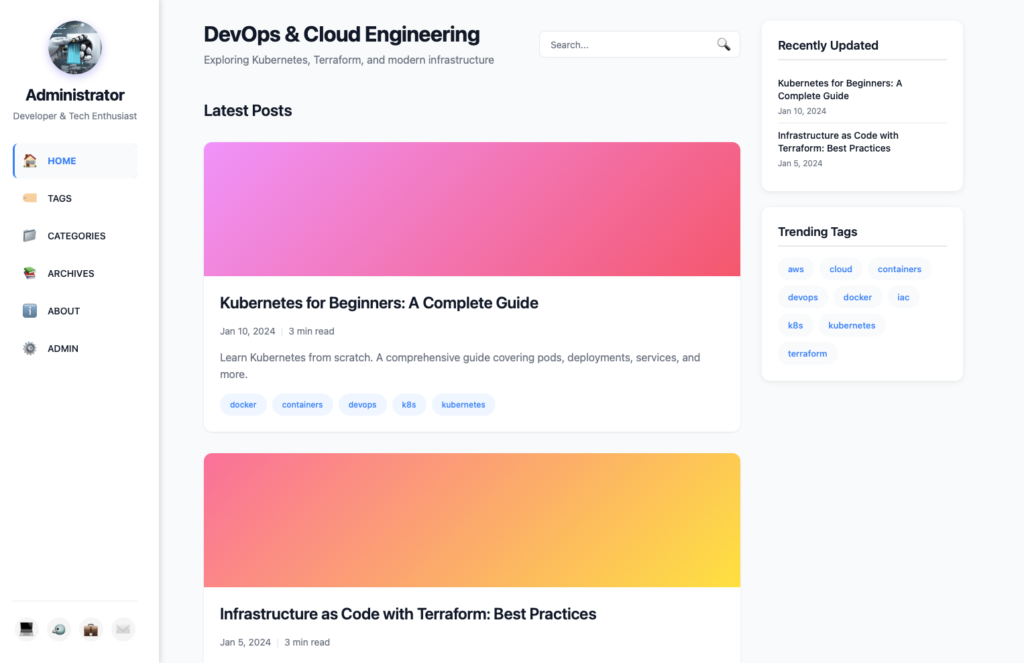
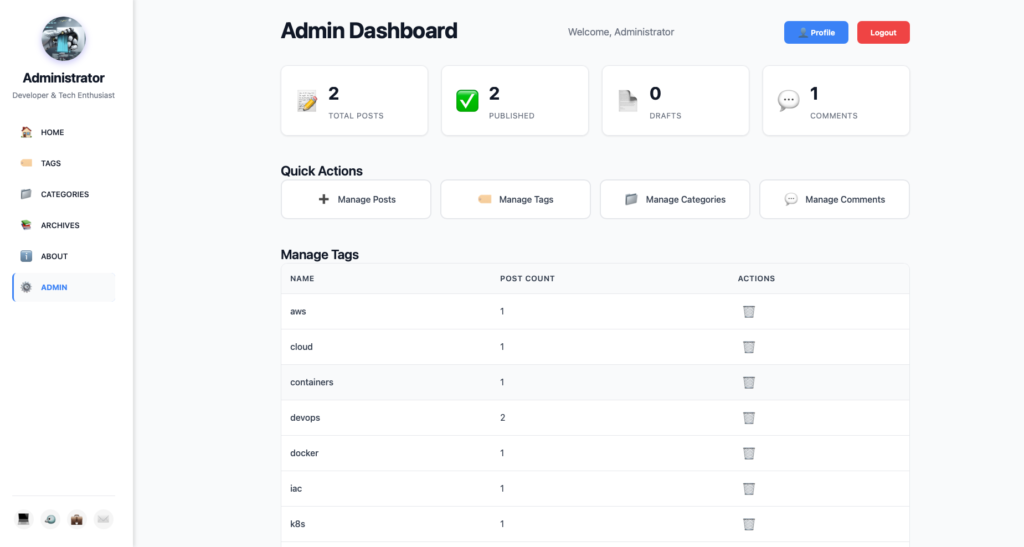
  5. Traffic through TraefikTraefik terminates TLS and routes readers to the blog and admins to the dashboard via /admin.
  6. Persistence with LonghornMongoDB runs as a StatefulSet on a 10 GiB Longhorn volume and survives pod restarts and cluster updates.

Screenshots and diagrams

GitLab CI/CD pipeline · GitOps with Argo CD: 21 resources, all healthy and synced · Blog application home page · Admin dashboard

Resources managed by Argo CD

  • Deployment nextjs-blog with 3 replicas and rolling updates
  • StatefulSet mongodb with a 10 GiB PVC on Longhorn
  • Service ClusterIP on port 3000 and Ingress through Traefik
  • ConfigMap and Secret for environment variables and credentials

Kustomize layout

k8s/
├── base/      deployment, service, ingress, configmap, secret, mongodb
└── overlays/
    ├── dev/   kustomization.yaml
    └── prod/  kustomization.yaml, replica-patch.yaml

Container security

  • Non-root user at runtime
  • Alpine base with a minimal attack surface
  • No dev dependencies in the final image
  • Trivy scan in every pipeline

Results

  • Complete CI/CD pipeline with 14 jobs in 6 stages
  • GitOps deployment with Argo CD and auto-sync
  • Security scanning with Trivy, SAST and OWASP ZAP
  • Zero-downtime deployments with health checks
  • Persistent storage with Longhorn
  • Role-based access control with 4 roles and JWT authentication

Client feedback

I had the pleasure of working with Elmehdi on our infrastructure modernization project for us over four months. He is an incredibly skilled professional who brought deep Kubernetes and automation expertise to our team. I was particularly impressed by his ability to build a complete production-grade Kubernetes platform that reduced our deployment time.
Ismail HamdiHamdiservices, Montréal · LinkedIn recommendation, February 2026View on LinkedIn →

Planning something similar?

I support teams across the DACH region and French-speaking countries, remotely or on-site around Stuttgart.