Skip to content Skip to footer

Air-Gapped Kubernetes: The Ultimate Guide to Isolated Cluster Deployments

Air-Gapped Kubernetes: The Ultimate Guide to Isolated Cluster Deployments

In security-critical environments like defense, finance, and healthcare, exposing your Kubernetes cluster to the internet isn't just risky—it's often prohibited. Air-gapped Kubernetes deployments provide the ultimate isolation, running completely disconnected from external networks while still delivering the power and flexibility of cloud-native orchestration.

What is Air-Gapped Kubernetes?

An air-gapped Kubernetes cluster is a completely isolated container orchestration environment with zero network connectivity to the internet or other external networks. Think of it as a digital fortress—nothing comes in, nothing goes out, except through strictly controlled physical or logical channels.

Unlike traditional Kubernetes deployments that pull container images from public registries, fetch charts from Helm repositories, and download updates automatically, air-gapped clusters must be entirely self-sufficient. Every dependency, from container images to Kubernetes binaries, must be pre-loaded or transferred through secure offline mechanisms.

Air-Gapped Kubernetes - High Level Architecture
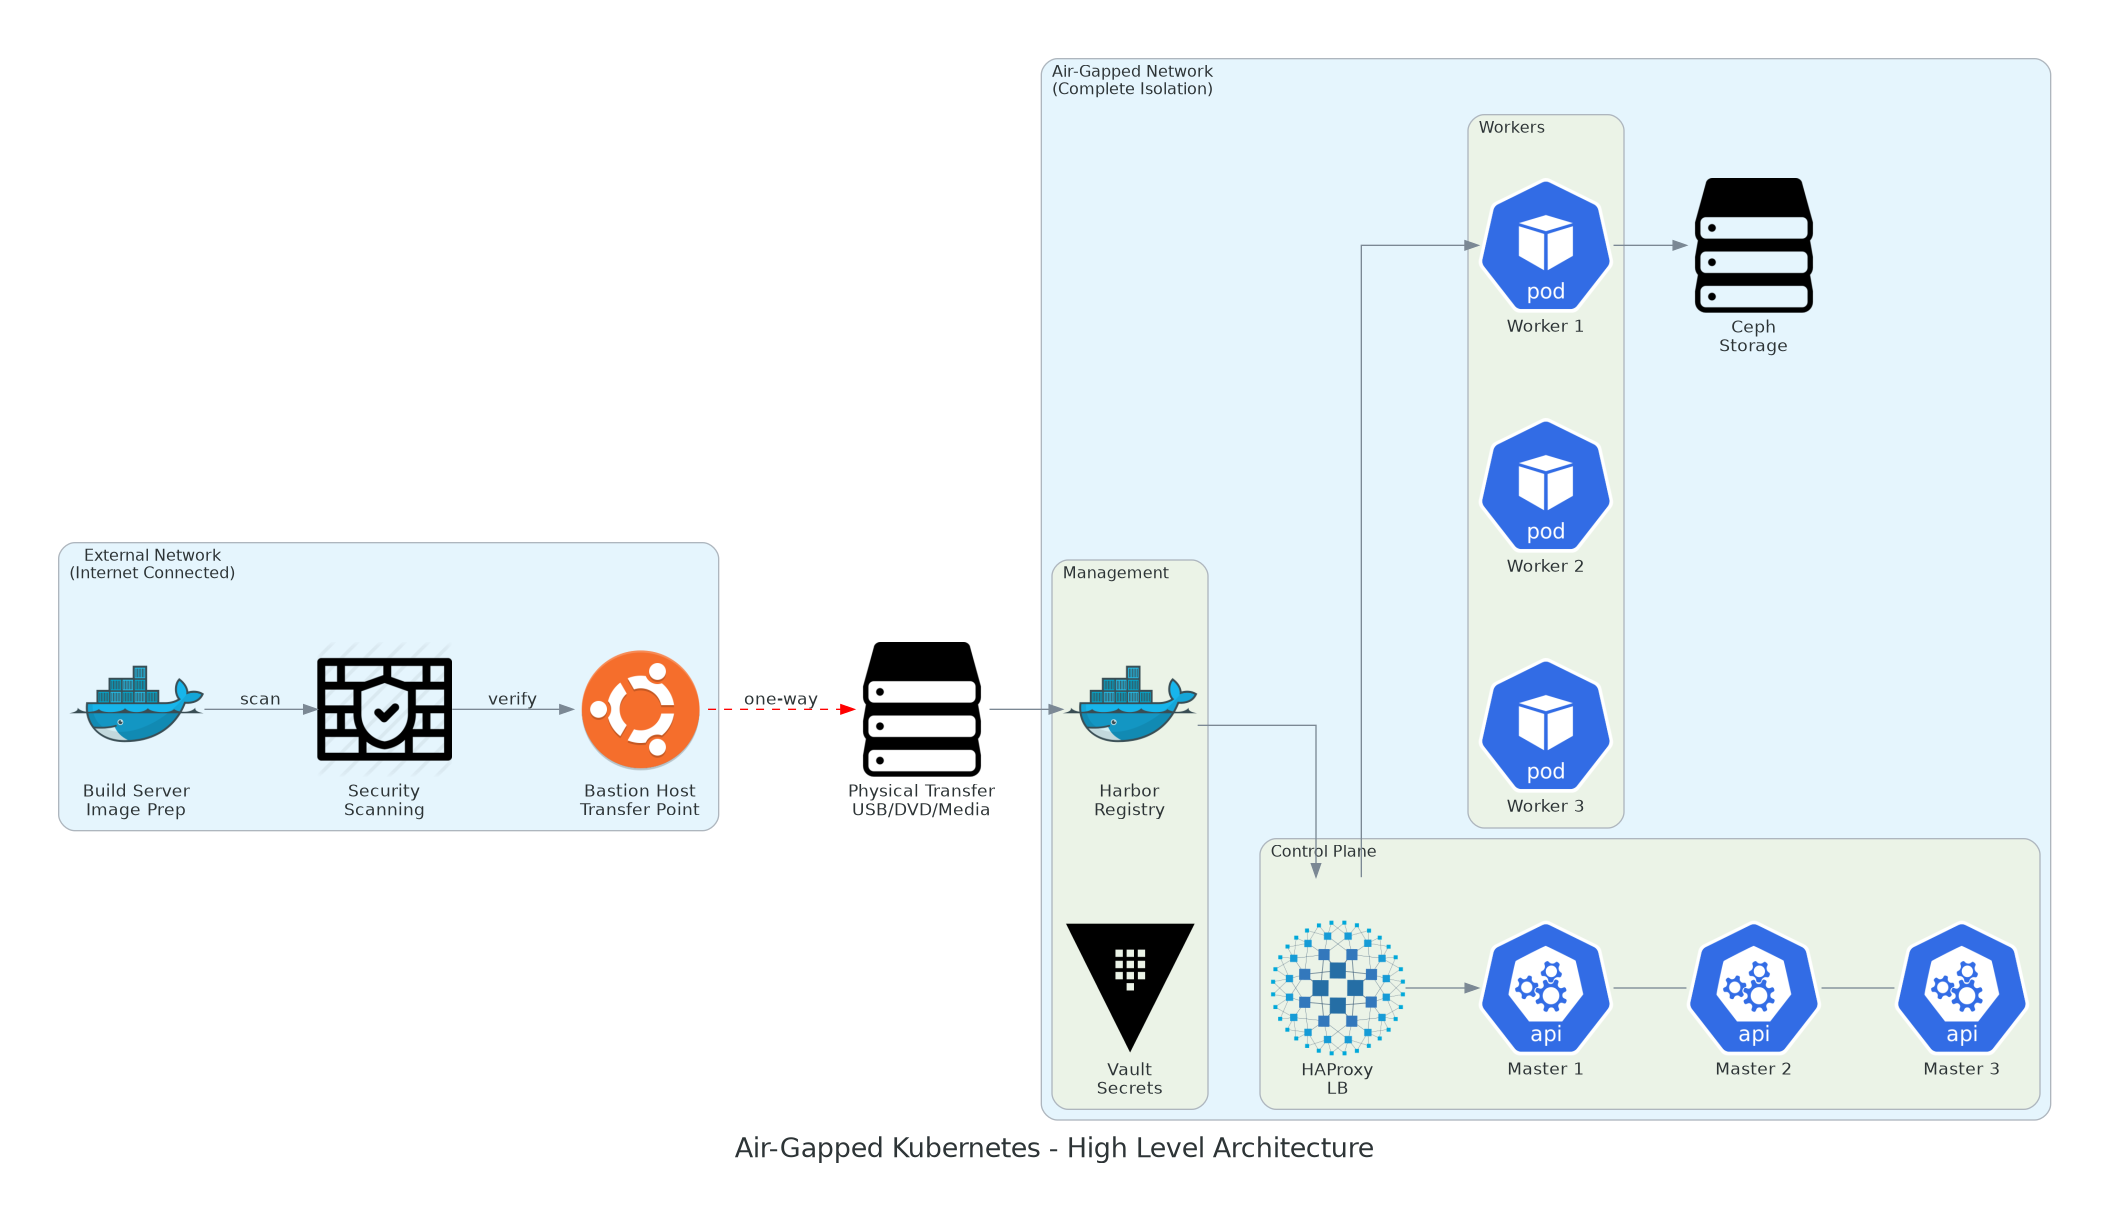
Air-Gapped Kubernetes High Level Architecture

Complete air-gapped architecture showing external preparation, secure transfer mechanism, and isolated internal infrastructure

Key Characteristic

Air-gapped doesn't just mean "no internet." It means complete network isolation from any untrusted network. This includes disconnection from corporate networks, cloud providers, and even other internal networks that could potentially be compromised.

The Anatomy of Air-Gapped Architecture

An air-gapped Kubernetes environment consists of several critical components working together in isolation:

Private Container Registry

A self-hosted registry (Harbor, Nexus, or JFrog Artifactory) that stores all container images locally. No external registry access allowed.

Internal Package Mirrors

Local mirrors of OS packages, Helm charts, and application dependencies. Critical for updates and new deployments.

Certificate Authority

Internal PKI infrastructure for generating and managing all TLS certificates without external certificate authorities.

Disconnected Nodes

Kubernetes control plane and worker nodes with all network interfaces restricted to internal cluster communication only.

When Do You Need Air-Gapped Kubernetes?

Air-gapped deployments aren't for everyone. They introduce significant operational complexity and require careful planning. However, they're essential in specific scenarios:

1. Regulatory Compliance Requirements

Industries with stringent data protection regulations often mandate air-gapped infrastructure:

Industry Regulation Air-Gap Requirement
Defense & Military ITAR, CMMC Level 5 Mandatory for classified systems
Financial Services PCI-DSS, SOX Required for critical financial data
Healthcare HIPAA, HITECH Recommended for PHI processing
Government FedRAMP High, IL5/IL6 Required for sensitive government data
Critical Infrastructure NERC CIP, TSA Security Directives Mandatory for OT/ICS environments

2. National Security & Defense

Military installations, intelligence agencies, and defense contractors require air-gapped systems to protect classified information and maintain operational security. These environments often operate at Impact Level 5 or 6, where any network connectivity could pose a national security risk.

3. Critical Infrastructure Protection

Power grids, water treatment facilities, nuclear plants, and transportation systems use air-gapped Kubernetes to isolate operational technology (OT) from information technology (IT) networks. A breach in these systems could have catastrophic real-world consequences.

Real-World Example: Stuxnet

The Stuxnet worm demonstrated that even air-gapped systems can be compromised through infected USB drives. This led to the destruction of Iranian nuclear centrifuges despite the facilities being completely isolated from the internet. Modern air-gapped deployments must account for both digital AND physical security.

Air-Gapped Kubernetes Architecture Deep Dive

Let's explore the technical architecture of a production-ready air-gapped Kubernetes deployment.

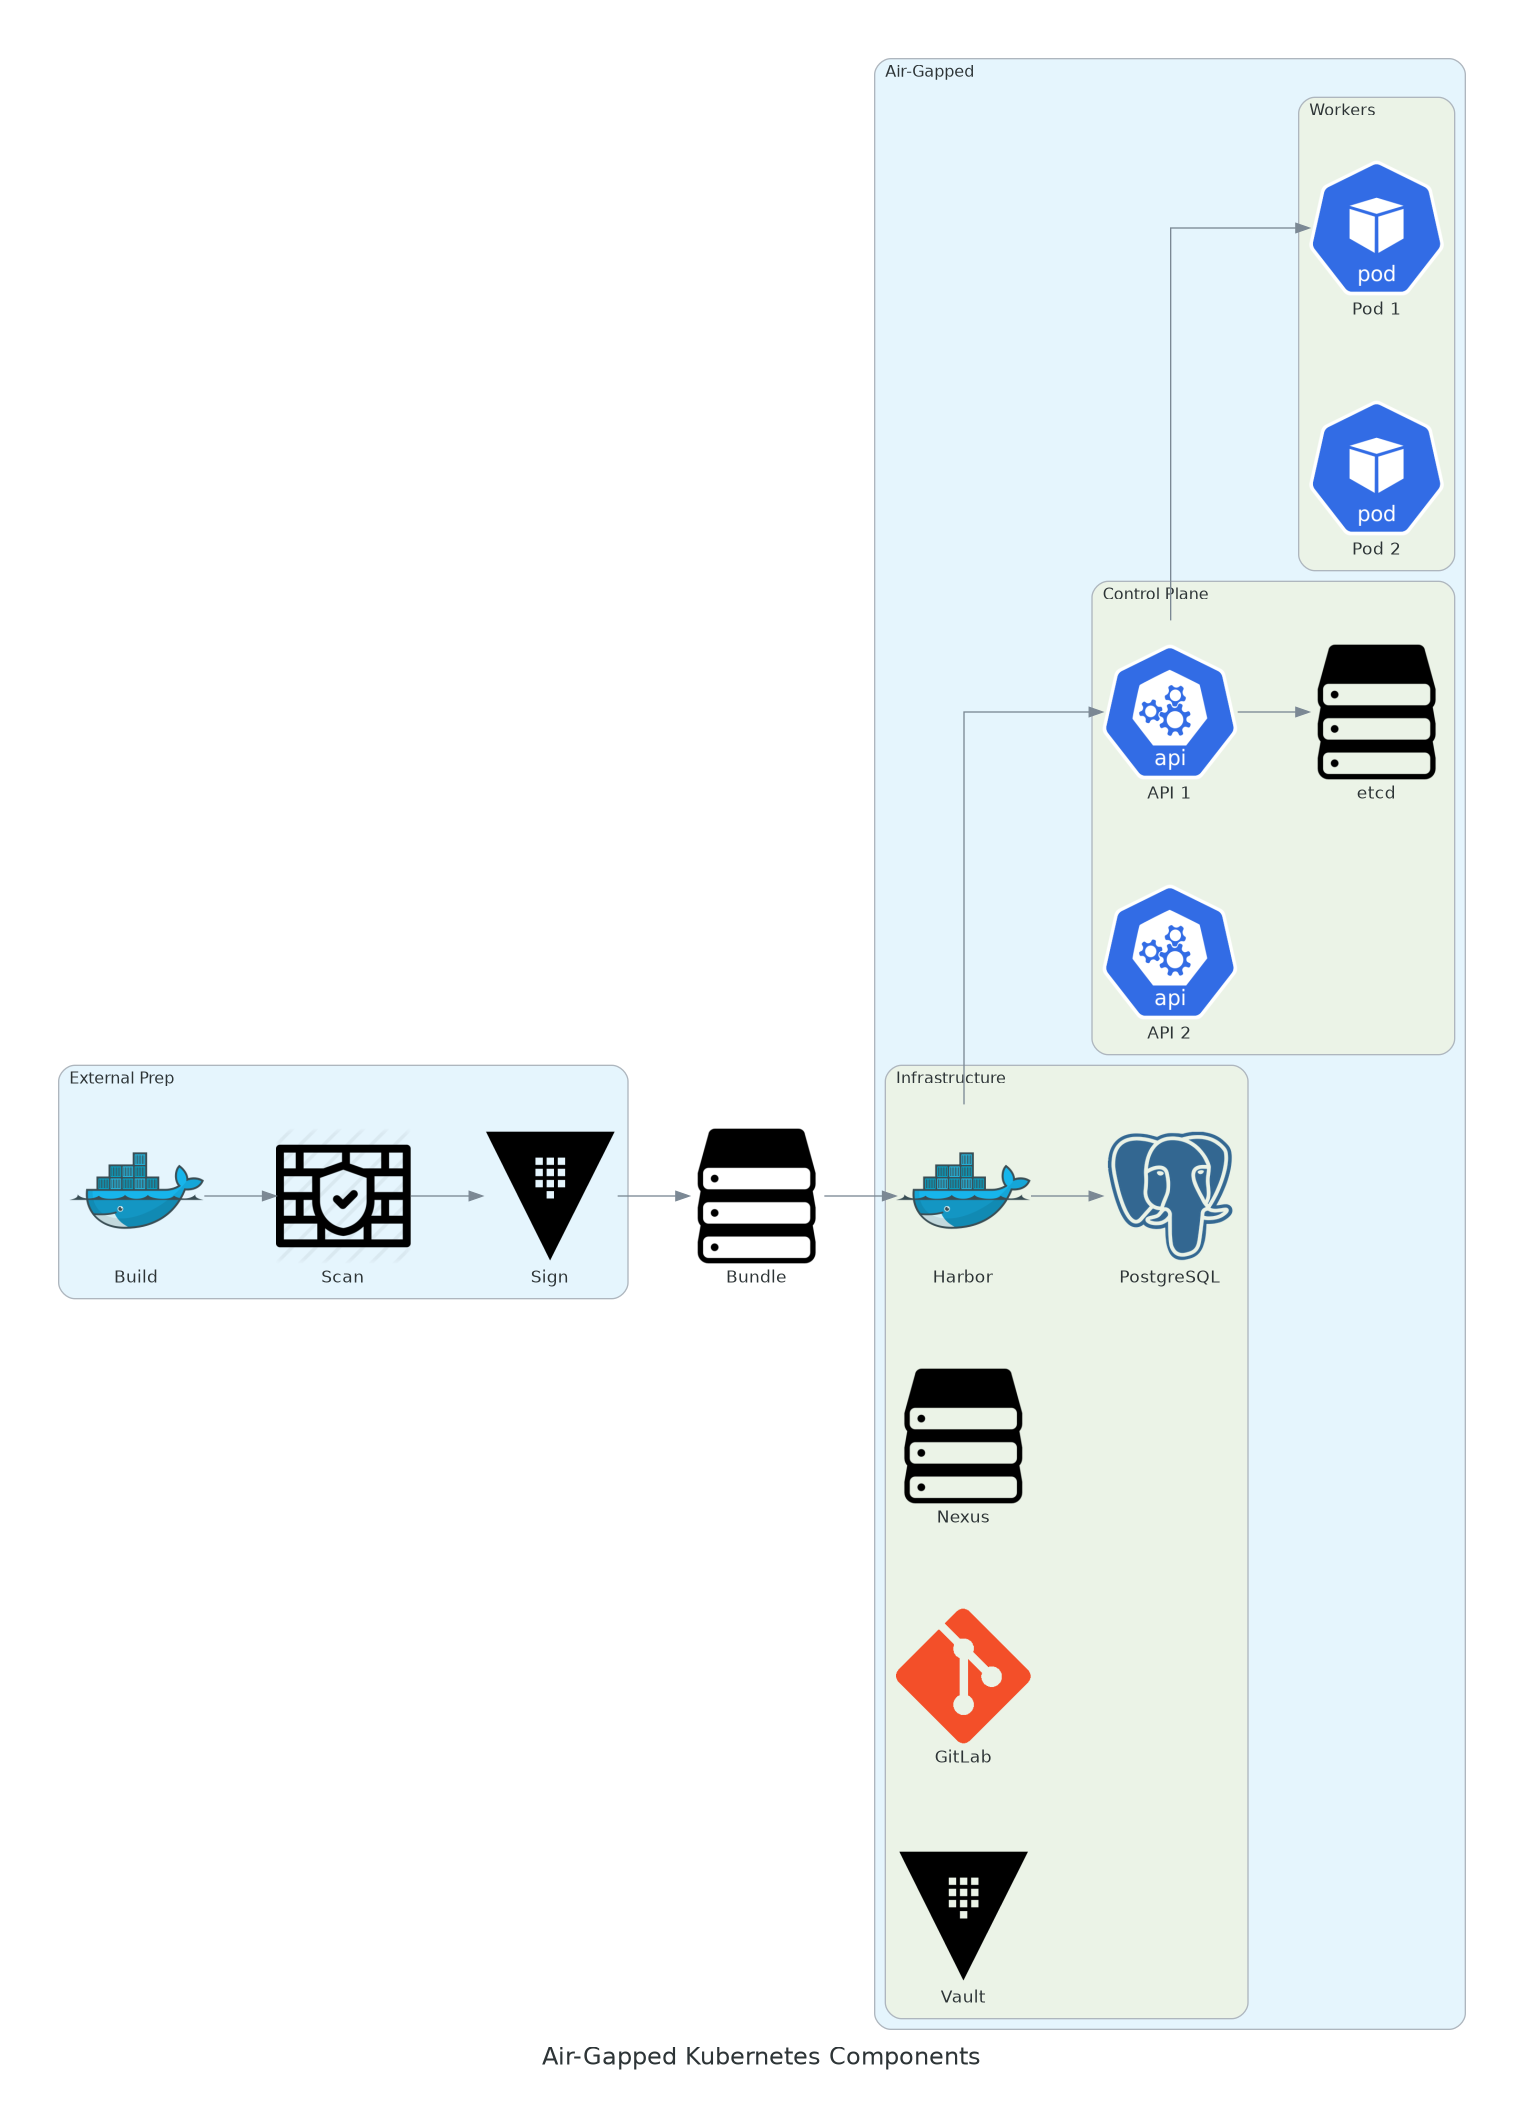
Complete Component Architecture

Air-Gapped Kubernetes Component Architecture

Detailed view of all components including infrastructure services, control plane, and worker nodes

Network Flow and Security Zones
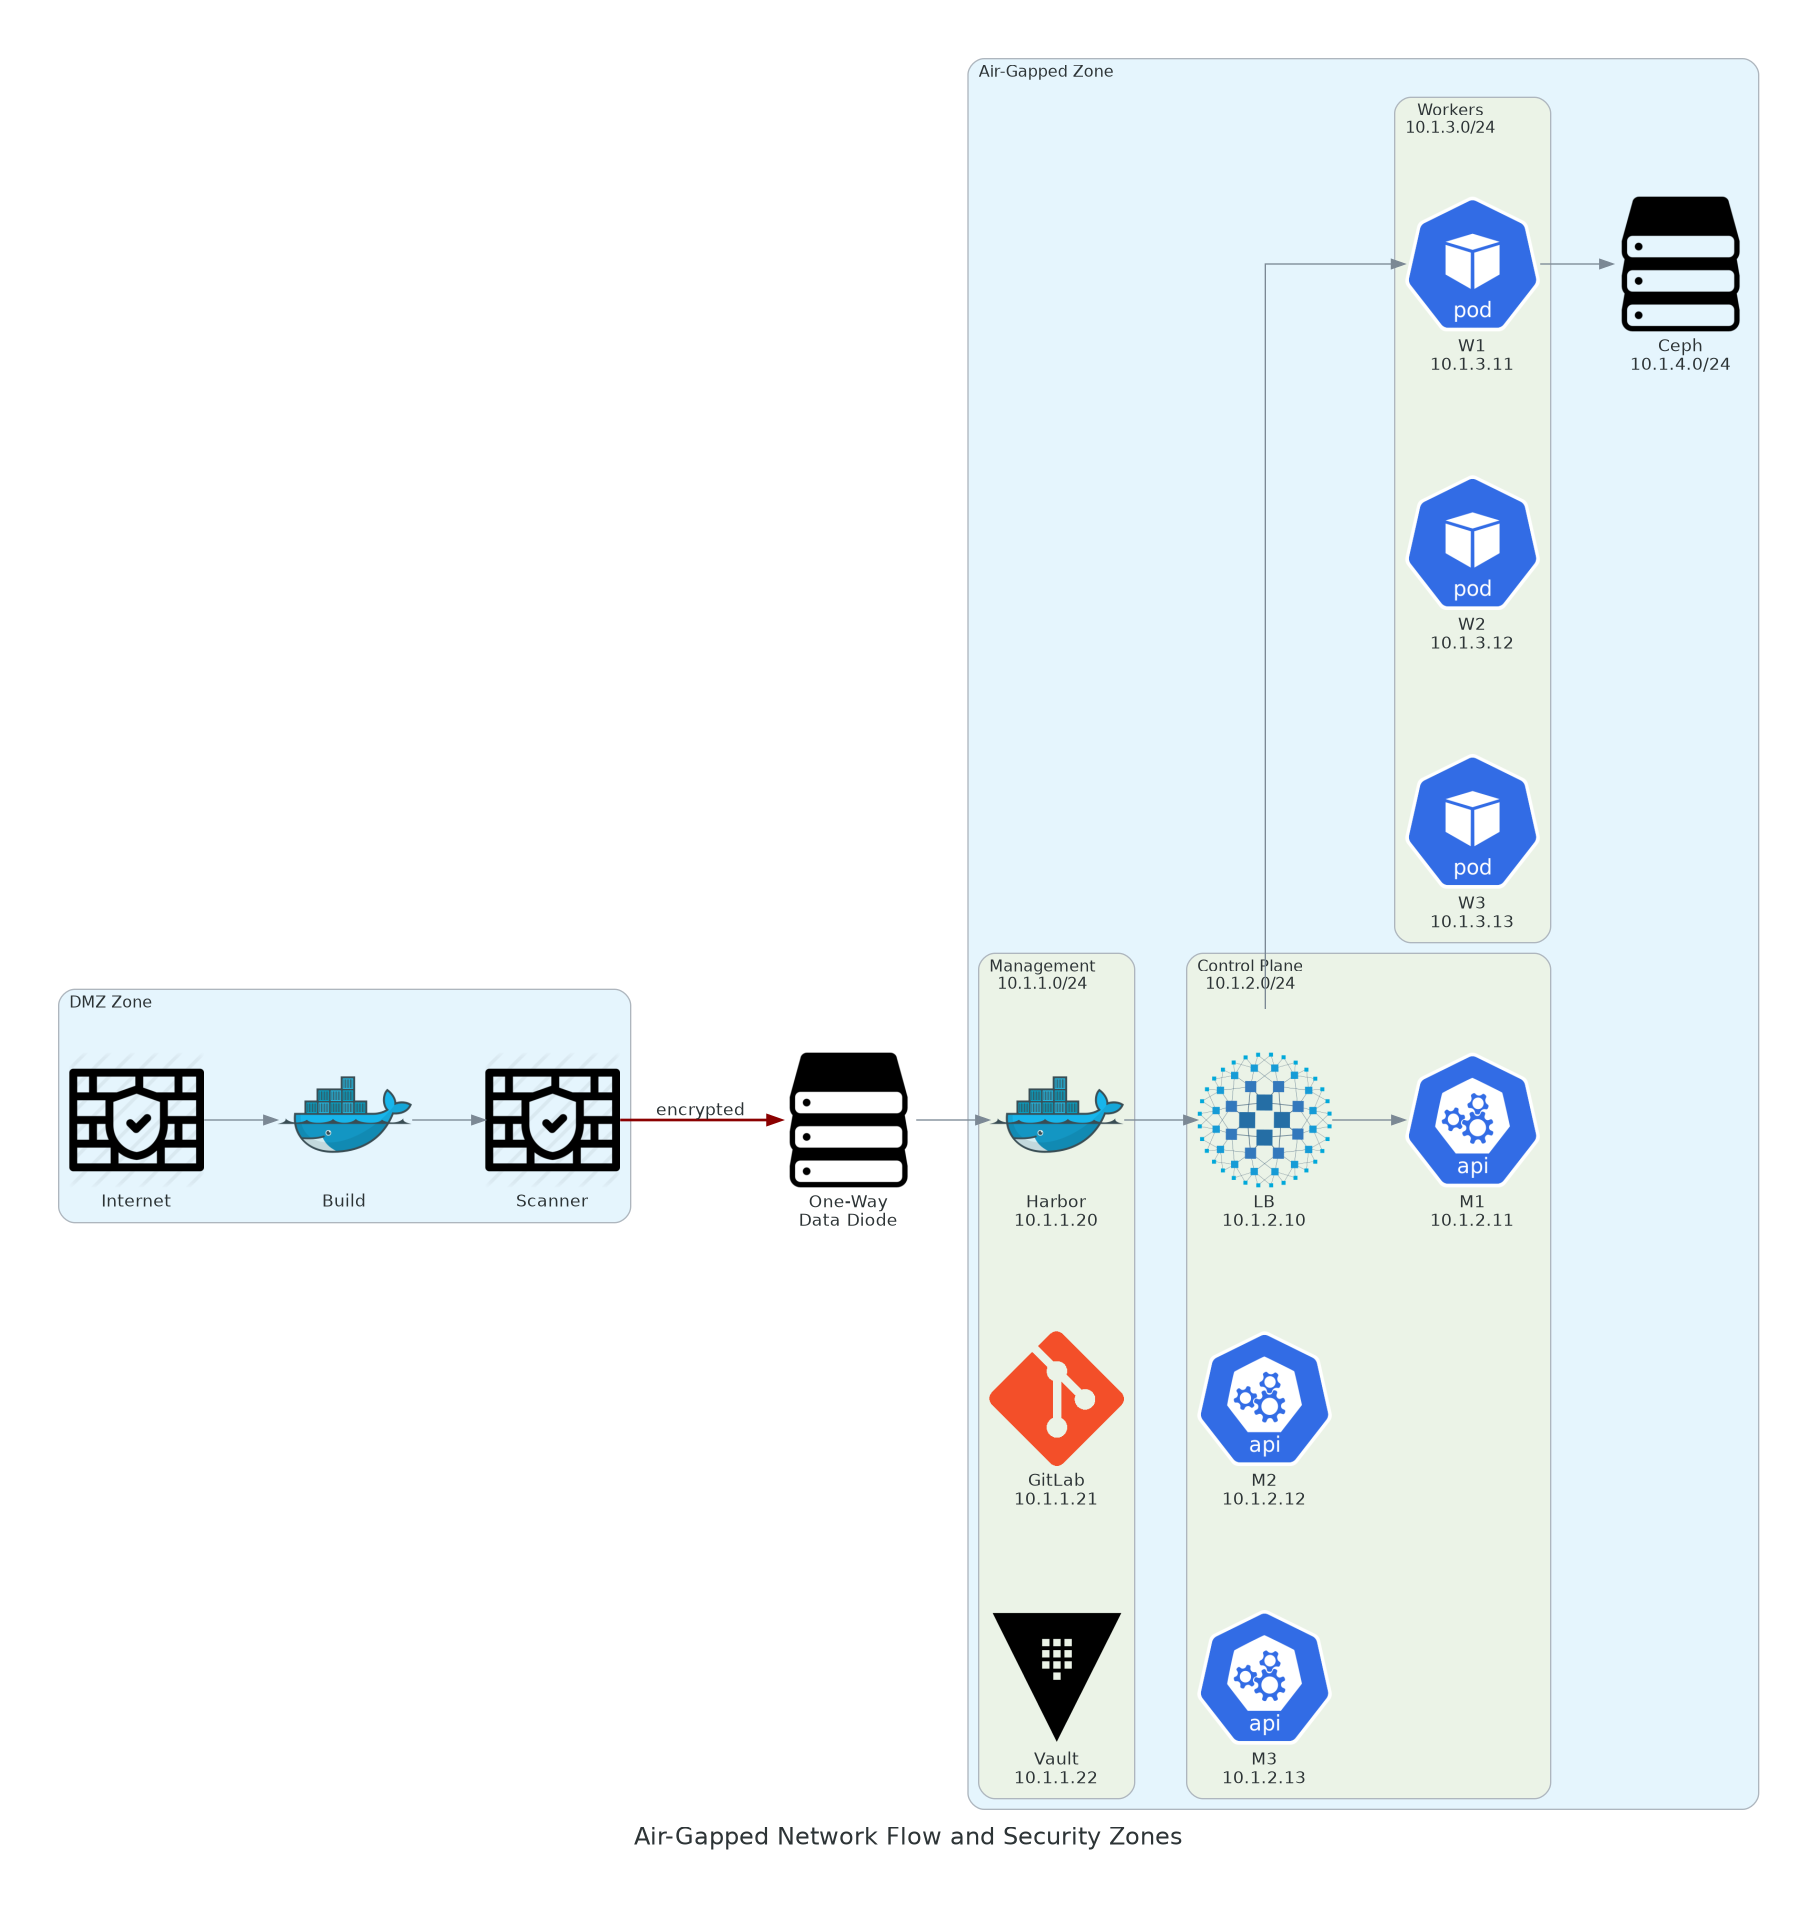
Air-Gapped Network Flow

Network segmentation showing DMZ, one-way data diode, and internal subnet isolation

Component Breakdown

1 External Build Zone

This internet-connected environment is where you prepare all artifacts for transfer to the air-gapped network:

  • Container Image Building: Pull base images, build application containers, scan for vulnerabilities
  • Dependency Collection: Download all required packages, Helm charts, and binaries
  • Security Scanning: Perform vulnerability assessments before transfer
  • Artifact Packaging: Bundle everything into signed, verified archives

2 Secure Transfer Mechanism

The critical bridge between connected and air-gapped environments:

  • Physical Media: Encrypted USB drives, DVDs, or hard drives
  • Bastion Host: Dedicated transfer server with strict security controls
  • One-Way Data Diodes: Hardware-enforced unidirectional data flow
  • Verification Process: Checksum validation, signature verification, malware scanning

3 Management Cluster

Internal services that replace external dependencies:

  • Harbor Registry: Stores all container images with vulnerability scanning and signing
  • Nexus/Artifactory: Hosts Helm charts, OS packages, and application binaries
  • Internal Git: Source code repository (Gitea, GitLab CE)
  • HashiCorp Vault: Secrets management and certificate authority
  • DNS/DHCP/NTP: Essential network services for cluster operation

4 Kubernetes Control Plane

High-availability control plane architecture:

  • 3+ Master Nodes: Running API server, scheduler, and controller manager
  • etcd Cluster: Distributed key-value store for cluster state (must be odd number of nodes)
  • Internal Load Balancer: HAProxy or Keepalived for HA API endpoint
  • No External Dependencies: All components pull from internal registry

5 Worker Nodes

Application runtime environment:

  • Container Runtime: containerd or CRI-O configured to use internal registry
  • Node Policies: Strict network policies preventing external communication
  • Local Storage: Direct-attached storage or distributed storage for persistence
  • Resource Isolation: CPU, memory, and network quotas per namespace

Building an Air-Gapped Kubernetes Cluster

Let's walk through the practical implementation of an air-gapped Kubernetes cluster from scratch.

Download Kubernetes Components

#!/bin/bash
# Download Kubernetes binaries for air-gapped deployment
K8S_VERSION="v1.29.0"
ARCH="amd64"

# Create directory structure
mkdir -p airgap-bundle/{binaries,images,charts,packages}

# Download kubeadm, kubelet, kubectl
cd airgap-bundle/binaries
wget https://dl.k8s.io/release/${K8S_VERSION}/bin/linux/${ARCH}/kubeadm
wget https://dl.k8s.io/release/${K8S_VERSION}/bin/linux/${ARCH}/kubelet
wget https://dl.k8s.io/release/${K8S_VERSION}/bin/linux/${ARCH}/kubectl

# Make binaries executable
chmod +x kubeadm kubelet kubectl

Bundle Size Considerations

A complete Kubernetes air-gap bundle typically ranges from 5-20 GB depending on included images and charts. Plan transfer media accordingly. For large deployments, consider splitting the bundle into manageable chunks with individual checksums.

Operational Practices and Management

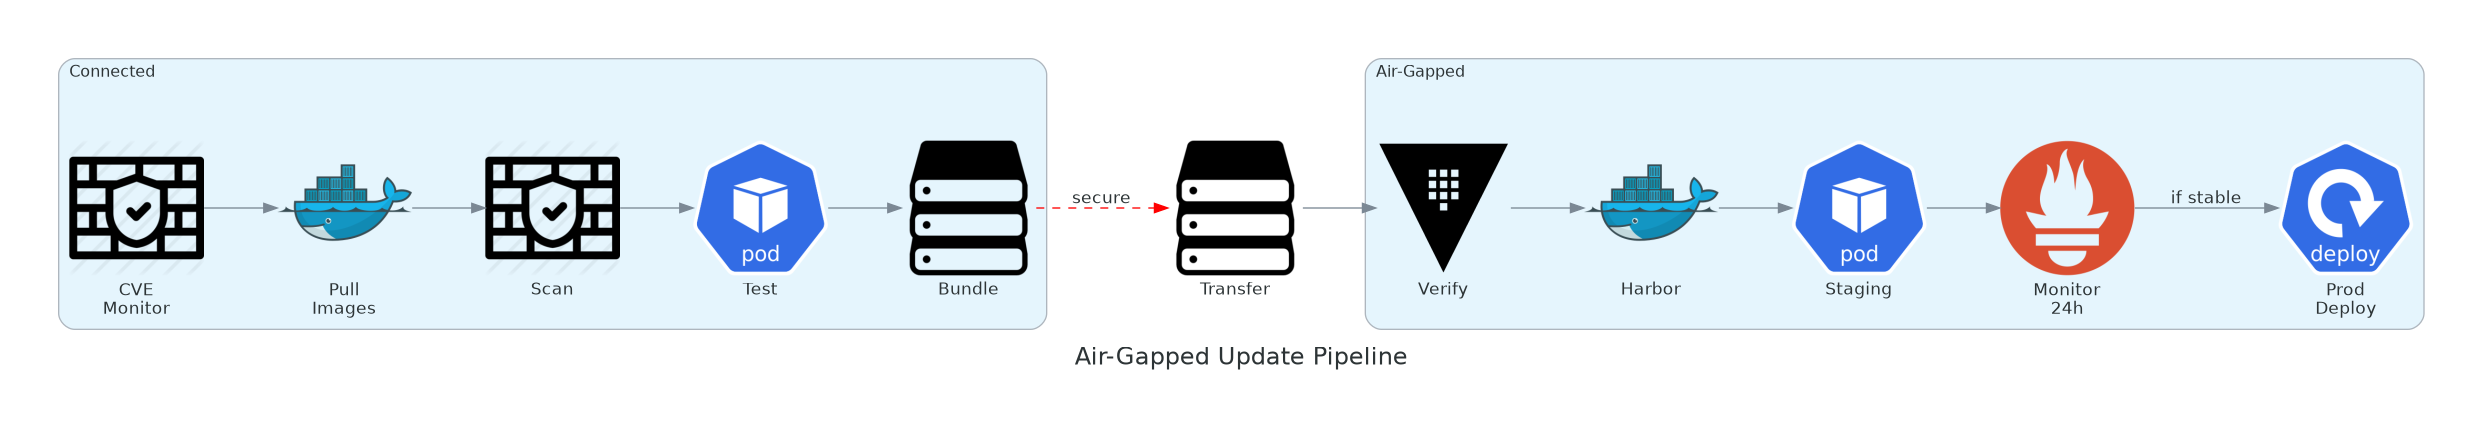
Update and Deployment Pipeline

Air-Gapped Update Pipeline

Complete workflow for security updates from CVE monitoring through staging to production deployment

Self-Hosted Monitoring Stack
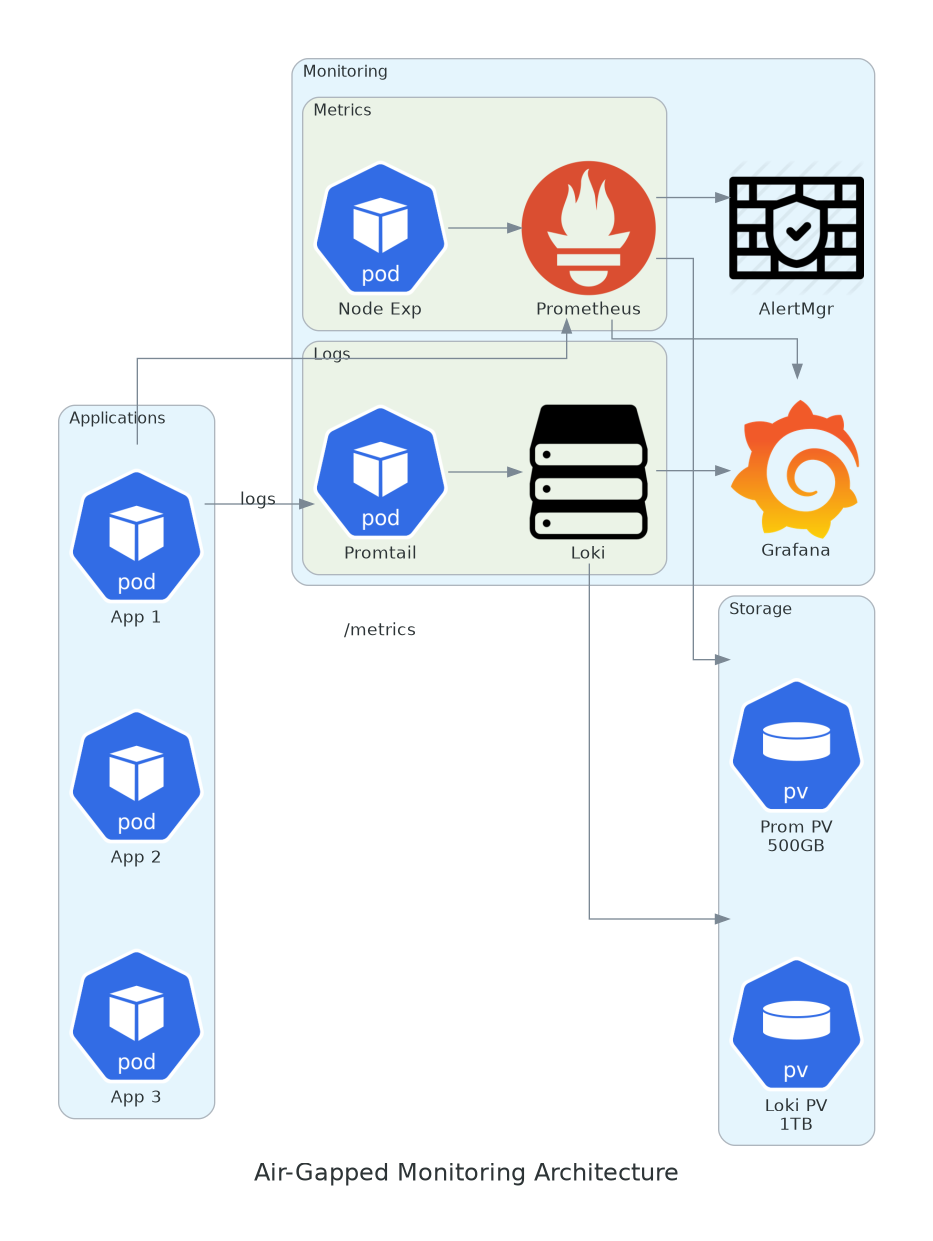
Air-Gapped Monitoring Architecture

Complete observability stack with Prometheus, Loki, Grafana, and Alertmanager

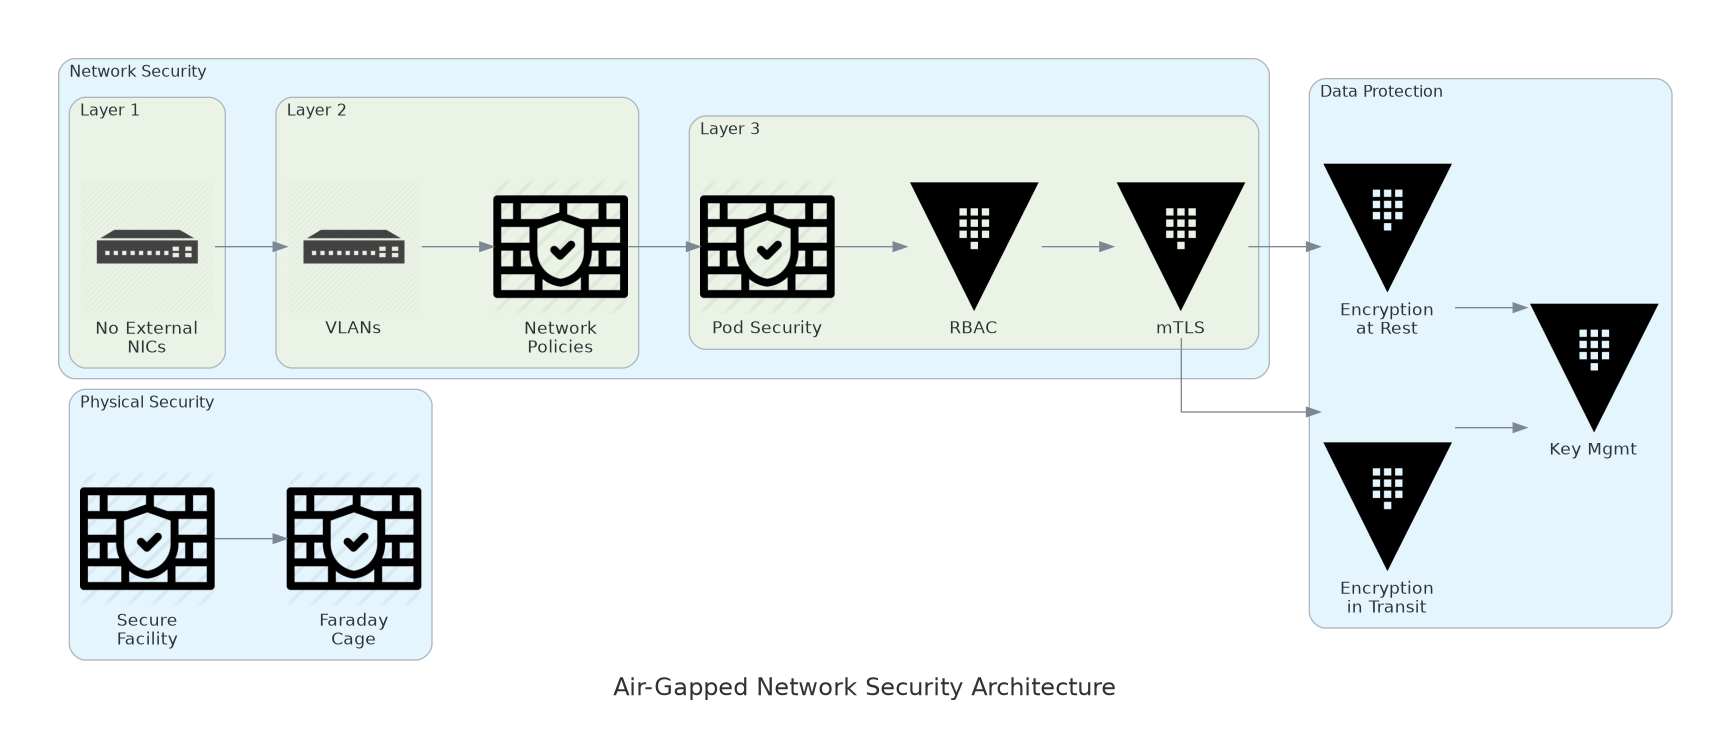
Network Security Architecture

Multi-Layer Security Architecture

Air-Gapped Security Architecture

Defense-in-depth security with physical isolation, network segmentation, and application-level controls

Security Best Practices

1. Physical Security

Secure facility access, Faraday cages for TEMPEST protection, disabled physical ports, and comprehensive physical audit logs.

2. Network Segmentation

VLANs per namespace, Kubernetes Network Policies enforcing zero-trust, and complete isolation between subnets.

3. Encryption Everywhere

Encryption at rest with Ceph, mTLS for all pod-to-pod communication, and HashiCorp Vault for key management.

4. Audit & Compliance

Immutable audit logs, Falco for runtime security, comprehensive RBAC policies, and Pod Security Standards.

Disaster Recovery Architecture

Disaster Recovery and Business Continuity
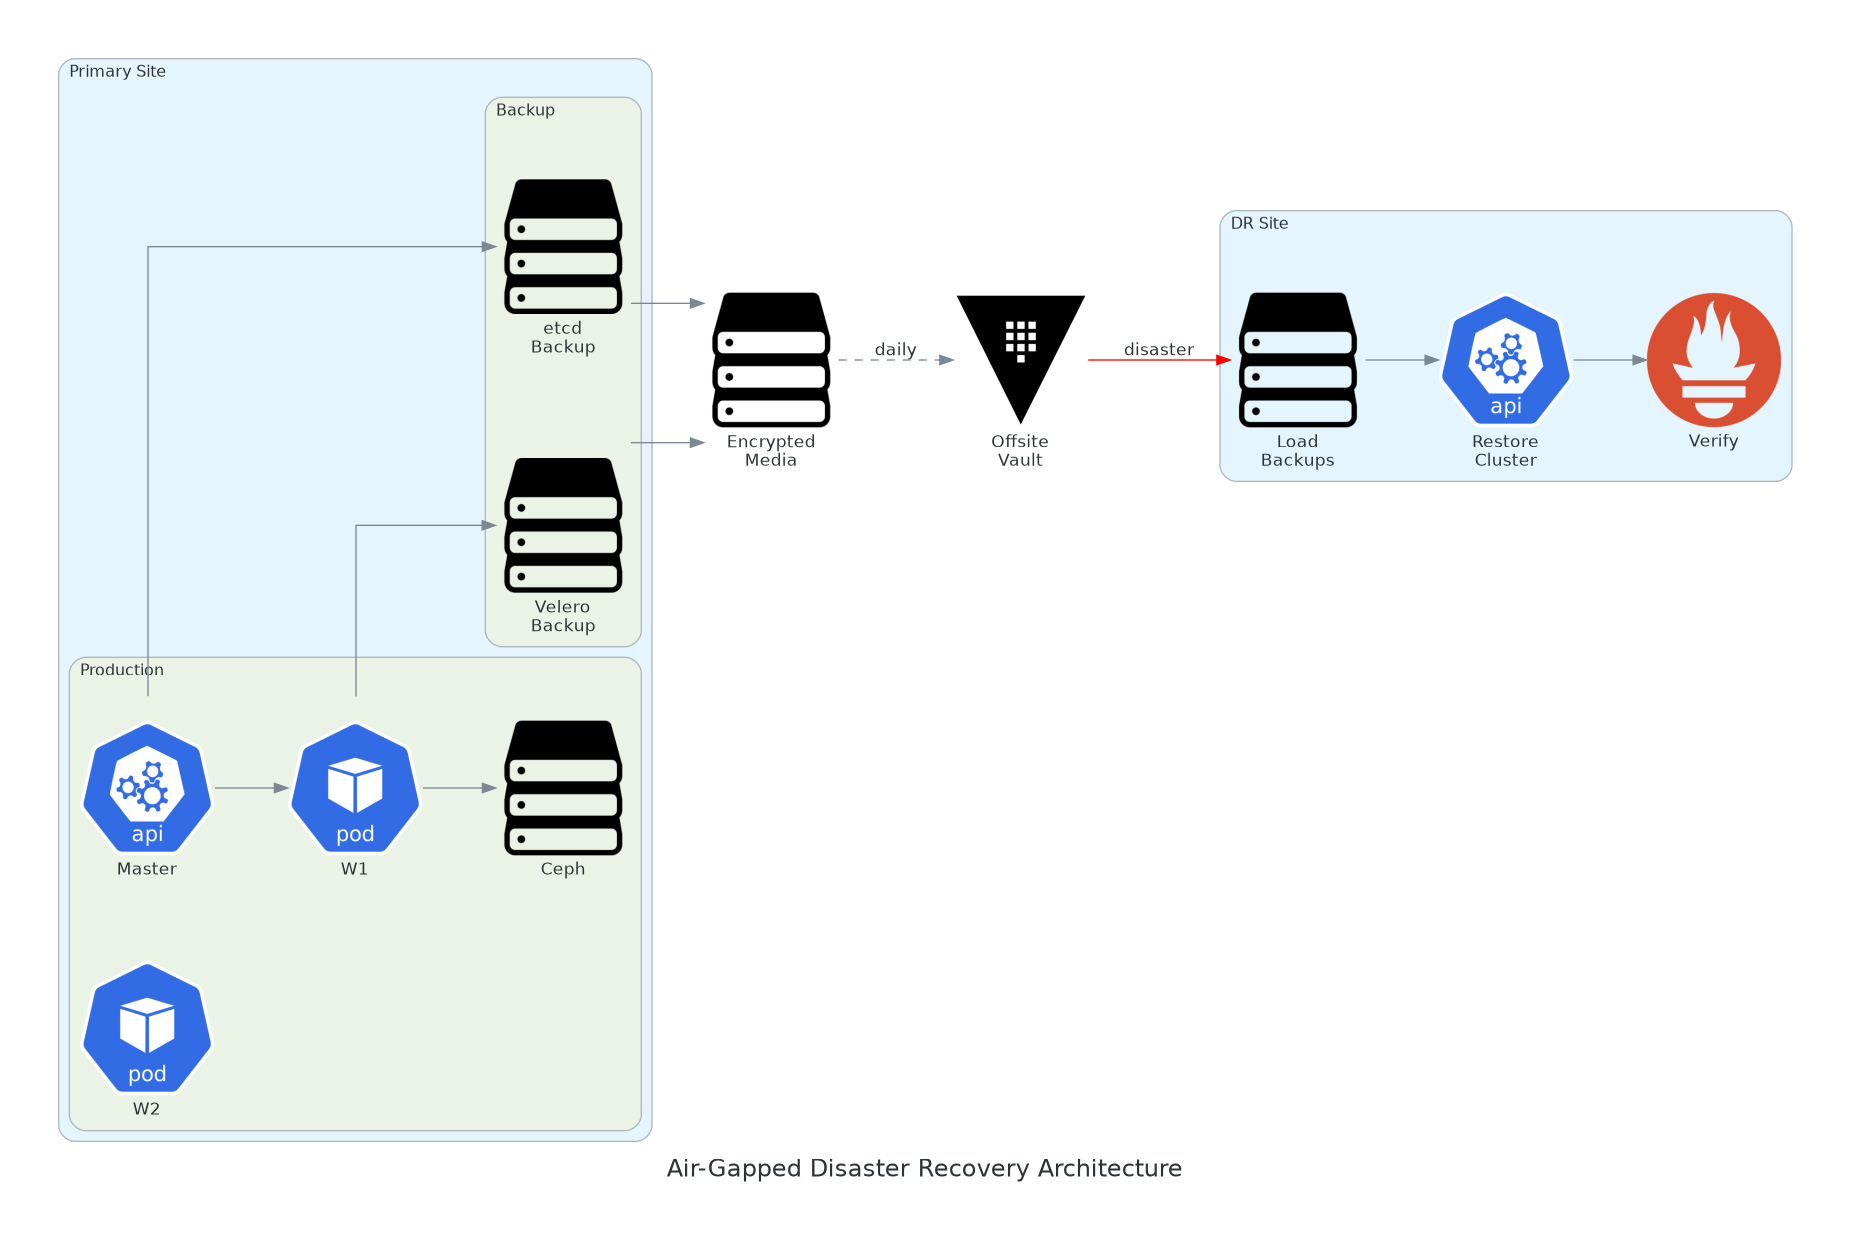
Air-Gapped Disaster Recovery

Complete DR strategy with automated backups, encrypted transport, and cold standby infrastructure
When Air-Gapped Kubernetes is Overkill

Cost Reality Check

Air-gapped Kubernetes deployments typically cost 3-5x more than equivalent cloud deployments when you factor in:

  • Additional staff for manual updates and transfers
  • Hardware procurement and maintenance
  • Dedicated security personnel
  • Slower time-to-market for new features
  • Complex disaster recovery procedures

Conclusion: Is Air-Gapped Kubernetes Right for You?

Air-gapped Kubernetes represents the apex of security isolation, but it's not a decision to make lightly. It's the right choice when:

  • Regulations mandate it: Defense, critical infrastructure, or classified data processing
  • Risk outweighs cost: The potential impact of a breach exceeds the 3-5x operational cost
  • No connectivity available: Remote locations with unreliable or non-existent internet
  • IP protection is paramount: Competitive advantage depends on absolute secrecy

Key Takeaways

  • Air-gapped Kubernetes is complete network isolation—no internet, no cloud, no external dependencies
  • Required for defense, critical infrastructure, and highest-security environments
  • Demands extensive planning: internal registries, package mirrors, CA infrastructure
  • Costs 3-5x more than cloud deployments due to operational overhead
  • Not just a technical challenge—requires process changes and dedicated staff
  • Most organizations don't need it—exhaust other security options first
"Air-gapped Kubernetes isn't about being paranoid—it's about understanding your threat model and choosing the right level of isolation for your risk profile. If your data's compromise could impact national security, critical infrastructure, or put lives at risk, air-gapped is the only answer. For everything else, there's probably a better way."

Have you implemented air-gapped Kubernetes in your environment?
What challenges did you face? Share your experiences in the comments below, or reach out to the ClusterCraftOPS team for consultation on securing your Kubernetes deployments.

Leave a Comment